4 articles found
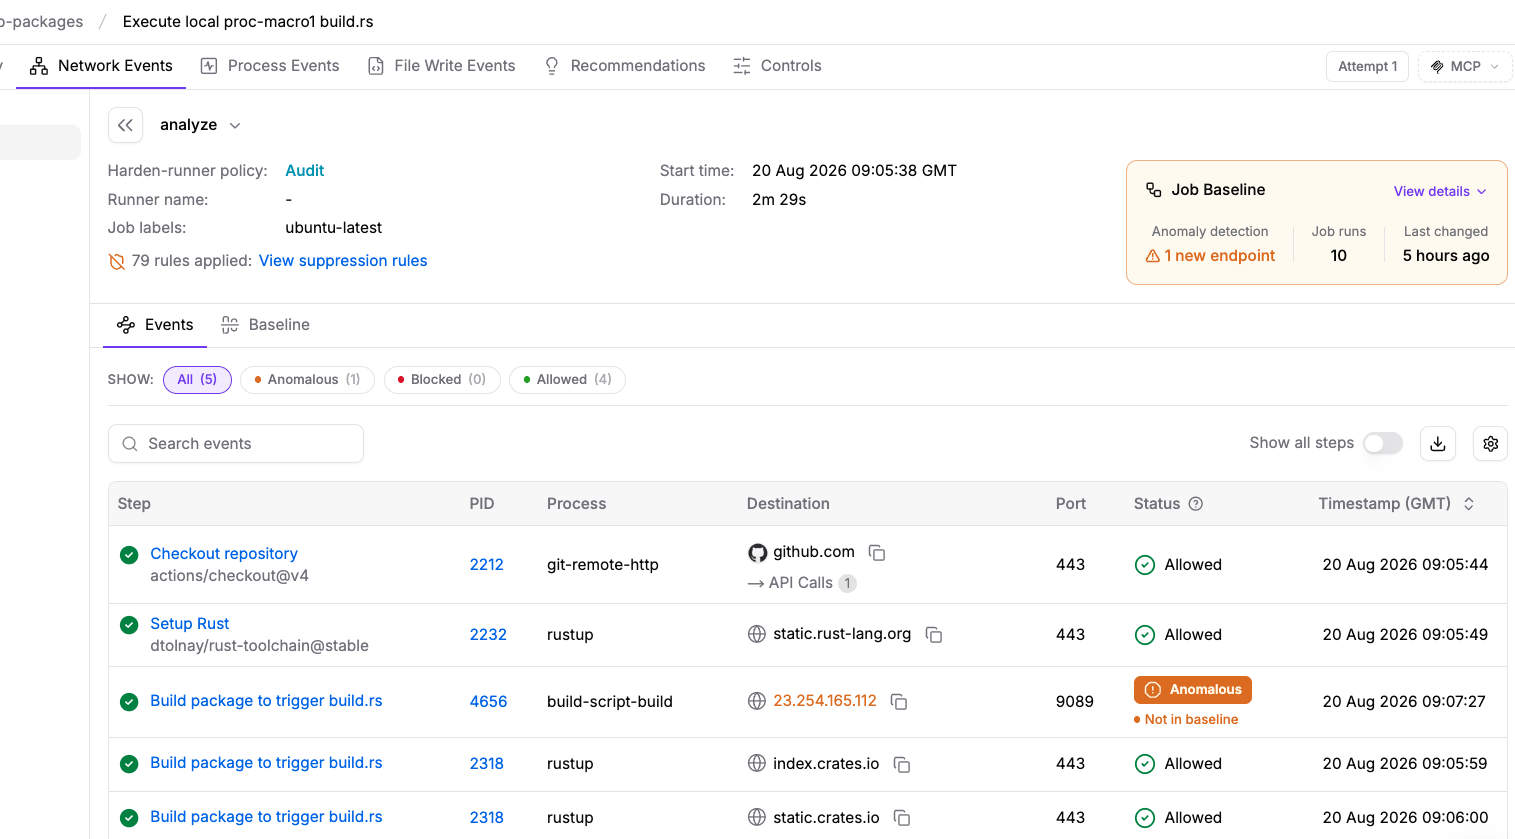
How the arrayref compromise turned a routine cargo update into silent RCE, weaponizing yanked versions as bait
How attackers turned Hugging Face and ClawHub into launchpads for infostealers, trojans, and cryptominers, and why your trust is the exploit.
The Litellm supply chain attack reveals a devastating blind spot in Python’s dependency model, malicious code that executes before you even import the package.
Over 1,000 packages compromised in a supply chain attack that exposed why our dependency ecosystem is fundamentally broken.