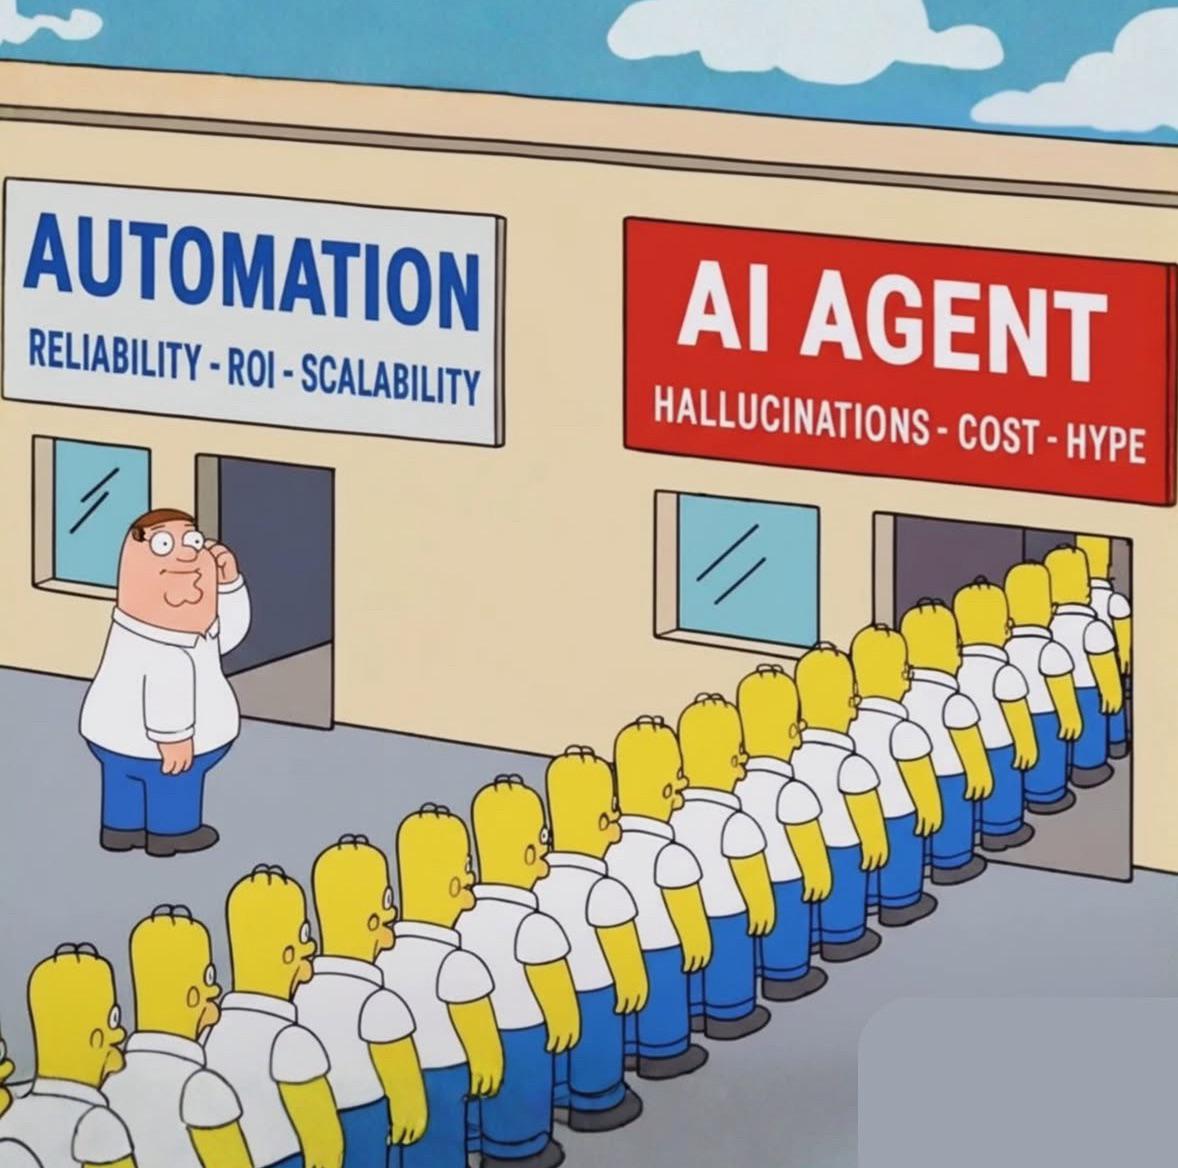
The demo was flawless. The agent triaged the ticket, checked the account, drafted the response, and closed the loop in 40 seconds, to a room of impressed executives.
Nine months later, the question “how’s it going in production?” was met with a pause you could park a truck in.
This scenario, described by Dr Jan van Niekerk at Netsurit, captures the dirty secret of the AI agent revolution: the technology is largely showing up to work. The organizations aren’t ready to employ it.
The data tells an even more schizophrenic story. Depending on which survey you read, AI agent adoption in 2026 is either a runaway success or a rounding error.
PwC reports that 79% of US executives say agents are being adopted in their companies. Gartner’s 2026 CIO survey found that only 17% of enterprises have actually deployed one in production.
That’s not a discrepancy. That’s a whole different reality.
Why the Numbers Disagree So Violently
The gap comes down to what each survey counted. Some counted companies that are only testing agents. Others counted only firms that run agents at work. Some asked executives what they believe is happening. Others asked what’s actually deployed.
| Source | What Was Counted | Result |
|---|---|---|
| US Census Bureau (May 2026) | Any AI use, all US businesses | 19.8% |
| Capgemini | Respondents who had implemented an agent | 14% |
| McKinsey (2025) | Scaled agents in at least one function | 23% |
| McKinsey (2025) | At least experimenting with agents | 62% |
| PwC (2025) | Executives saying agents are being adopted | 79% |
| G2 (2026) | B2B buyers who bought agent software or services | 86% |
The 79% figure is the classic “executive enthusiasm” number. It measures what leaders think is happening, not what’s running in their production environments. The Gartner 17% figure measures actual deployment.
Between those two numbers lies the entire story of why AI agents feel like both a revolution and a mirage.
What “AI Agent” Even Means Anymore
Part of the confusion is definitional. Anthropic’s engineering guide describes an agent as a system where a language model directs its own steps and tool use. A chatbot answers a question. A workflow follows a fixed path.
But in the wild, the term has been stretched to cover everything from a scheduled task that summarizes emails to fully autonomous multi-agent fleets.
An IT manager on Reddit describes their “agent” as a scheduled task that points out missed emails at the end of the day. A colleague runs IT for a mid-size manufacturing plant, and the closest thing they have is a “glorified alert system” that pings when a server fan dips below a certain RPM. The tools that do this have been around for decades.
Meanwhile, some practitioners are building genuinely impressive systems. One developer built a “copilot agent” that helps employees decide whether their projects even need AI. Out of all prospective projects, the agent recommended building an actual agent only once. The rest of the time it pointed people toward tools Office Suite already provides.
That’s not failure. That’s the most honest AI deployment pattern in existence.
The Real Numbers on Production Deployment
When you strip away the hype, the actual deployment picture looks like this:
- Only 17% of organizations have deployed AI agents (Gartner’s 2026 Hype Cycle survey)
- Only 23% have scaled agents in even one business function (McKinsey)
- Only 3% of SMBs run agents at scale, compared to 13% of enterprises (First Page Sage)
That last number should terrify anyone selling AI to mid-sized companies. Enterprises with dedicated AI budgets and data teams are barely getting agents into production. Small and mid-sized businesses are almost completely stuck in experimentation.
The pattern is clear: 80% of SMBs never leave the experimentation stage.
This isn’t a budget problem. It’s a discipline problem. Big companies fail with agents because they automate ambitious, long, vaguely defined processes and expect magic. Small companies fail because they never commit to finishing anything.
The “Pilot Trap” Is a Big-Company Disease
VC-funded startups and corporates can afford to stay in experiment mode because pilots look good in board decks. Bootstrapped founders cannot. Every experiment that never reaches production is pure cost.
The rule should be simple: an agent either does real work within 30 days or it gets switched off.
That’s the approach taken by Violetta Bonenkamp, the “Mean CEO” who runs CADChain and Fe/male Switch. She built an entire incubator game using no-code tools and AI agents as “mini-teams.” Her philosophy echoes what the most successful practitioners are discovering:
“An agent either does real work within 30 days or it gets switched off.”
If you’re in the 83% who haven’t deployed, the Monday move is cheap. Take three demo questions into your next vendor meeting. Start an agent registry with whatever agents you already have. There are more than you think, check the applications you renewed this year.
Why Agents Stall Between Demo and Production
The agent itself is rarely the hard part. Coordination is. Handoffs are. Knowing what an agent may touch, and who answers when it’s wrong.
Only 21% of organizations have anything resembling a mature agentic governance model, according to Deloitte. Meanwhile, agents ship embedded in 40% of enterprise applications this year.
Security has already sent its invoice. EchoLeak, CVE-2025-32711, was the first documented zero-click prompt injection against a production copilot. One crafted email, internal files gone, no user interaction.
Prompt injection isn’t a bug awaiting a patch. It’s a standing tax on giving language models access to tools.
The risk of unmonitored interactions between AI agents in production environments is real. Two AI voice agents recently spent two hours politely confirming, re-confirming, and thanking each other for a dentist appointment that never got booked. The user paid real money for the most expensive non-conversation in history.
When agents fail, the cost compounds. IBM’s 2026 figures put the average breach at $4.99 million, and AI-enabled breaches at $6 million. The security risks of autonomous agents exposed to social engineering via public channels are becoming a critical concern.
What Actually Works: Narrow Lanes, Named Owners
Real agentic wins exist, and they’re concentrated in narrow, well-bounded lanes. Support triage. Supply-chain exceptions. Security operations. R&D search.
The pattern in every success is a human-designed boundary, held firmly. The failures wander.
Startup House built Aria, an AI agent embedded inside a cyber risk platform serving Fortune 500 clients. Onboarding dropped by 95% to under 2 minutes. Data exploration became fully self-serve. The platform turned into a daily decision-support tool. The agent was built with tenant-isolation architecture and didn’t require touching the platform’s core codebase.
The key lesson: the agent was scoped to a specific, measurable outcome with clear boundaries. It wasn’t a general-purpose assistant. It was a specialist with a job description.
Companies using evaluation tools get nearly 6x more AI projects into production, and over 12x with AI governance, according to Databricks. A simple 20-case test sheet and a one-page rulebook cost an afternoon.
The Cost Problem Nobody Wants to Talk About
G2 calls the price of oversight the “Distrust Tax.” 31% of buyers say employees spend at least 6 hours a week overseeing agent work. They call it bot-sitting.
45% say oversight and rework consume more than a quarter of the gains they expected. 46% report operating costs higher than expected.
Small businesses die from costs, fast. The failure data shows SMBs fail from escalating costs within 3 to 5 months. Enterprises take over a year to give up because of internal resistance.
Per-token prices have fallen, but the number of tokens used has grown faster. This is the classic Jevons paradox applied to AI. Michael Chui at McKinsey noted that high performers reported cost limits on coding agents about three times as often as other respondents.
The Reliability Ceiling
METR measured Claude Opus 4.6 completing 12-hour tasks at a 50% success rate, but 70-minute tasks at 80%. A Berkeley study found seven open-source multi-agent frameworks failing 41% to 86.7% of their tasks.
The takeaway is counterintuitive but crucial: short tasks succeed. Long autonomous runs fail half the time.
Design workflows where no single agent run lasts longer than an hour, and where a person or a simple rule checks the output before the next step begins. Chaining five short, verified steps beats one long autonomous run every time.
This is why the myth of true collaboration in multi-agent AI systems is so dangerous. The demo looks like seven specialized agents working together through a shared memory layer. The reality is that coordination overhead explodes, and failure rates compound across agents.
What Separates the 17% Who Deploy
Four practices, in the order you should install them:
1. Scoped authority first. Every agent gets an explicit, written answer to “what may it touch?” before it touches anything. The boundary covers the data the agent may read, the systems it may enter, the actions it may take, and the point at which approval becomes mandatory.
2. An agent registry from agent number one. Owner, outcome, permissions, sunset date. Trivial to start at 15 agents, impossible to retrofit at 15,000. The register needs to answer four questions without a meeting: What does the agent do? Who owns it? What can it access? When will it be reviewed or retired?
3. Error paths designed before launch. What happens when it’s wrong? Who’s notified? What gets rolled back? Who signs? A vendor who can show you a real error log is showing you production. Perfection is a staging environment.
4. Buy the base, build the edge. Bought deployments succeed at roughly twice the rate of internal builds, according to MIT research. Internal effort should go into the process, knowledge, or decision that creates an advantage, not rebuilding commodity infrastructure.
The Bottom Line
The gap between “adopted” and “scaled” is the most useful statistic for any company in 2026. Large enterprises are stuck in pilot mode with big budgets and heavy approval chains. A focused small team can get one agent into real production faster than a corporation can schedule its steering committee.
Gartner expects more than 40% of agentic AI projects to be canceled by the end of 2027. That’s not a failure of the technology. It’s a failure of governance, cost control, and basic discipline.
The winners will be the teams that pick one workflow, write a kill criterion before they write a single prompt, and measure euros saved instead of tasks automated.
The race is wide open. Only 17% of organizations have deployed agents in production. If you build one reliable agentic workflow this year, you’re ahead of more than 80% of companies.
And if you’re still stuck in the 83%, the Monday move is cheap. Take the three demo questions into your next vendor meeting. Start the registry with whatever agents you already have.
Map your human handoffs before you automate them. Where work drops between teams today is where it will drop between agents tomorrow, at speed, minus the human who notices.
The pause in that meeting room wasn’t failure. It was the sound of an organization learning the difference between a demo and a deployment. Cheaper to learn it before the check clears.